#97930Harden distribution overview in extension manager
Frank Nägler 07/13/22, 19:54 updated 10/15/24, 09:30

Description
The distribution overview page is vulnerable for XSS.
If a distribution description contains XSS within the first 150 characters, the overview execute the code.
File: EXT:extensionmanager/Resources/Private/Partials/List/Distribution.html
Affected code: {distribution.description -> f:format.crop(maxCharacters: 150) -> f:format.raw()}
Reproduce: inject the code <script>alert('XSS');</script> to the description of an extension / distribution and open the overview.
Reviews 2

Related issues 1

Files 1
History 1821
-
Oliver Hader changed Field 12 Frank Nägler 07/13/22, 19:56
-
Oliver Hader changed Field 17 9.0, 10, 11 07/13/22, 19:58
-
Oliver Hader changed Related to #82000 07/13/22, 19:59
-
Oliver Hader changed TYPO3 Version
129 07/13/22, 19:59 -
Oliver Hader commented 07/25/22, 10:57
-
Frank Nägler commented 07/25/22, 11:00
I tested it by changing the data directly in the database. I guess, that there is no filter in the upload process.
-
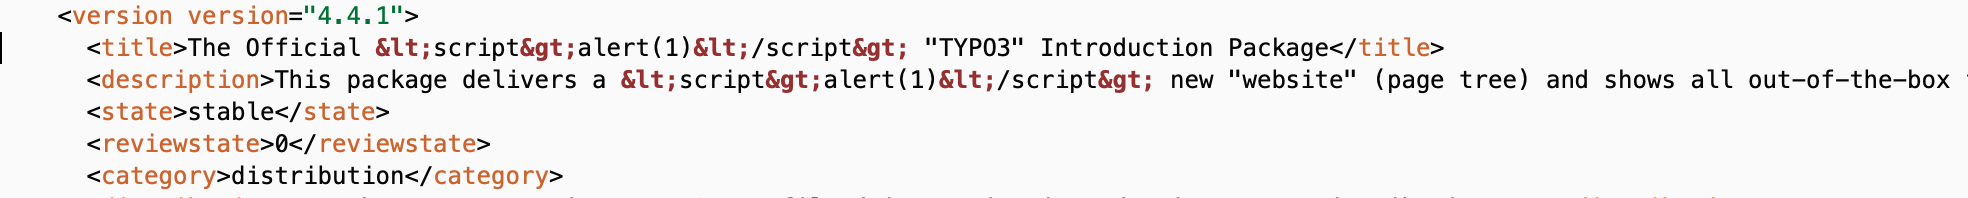
Oliver Hader commented and changed attached exteions.xml.gz.png 07/25/22, 11:11
extenions.xml.gzcontents are imported as is into the database → XSS confirmed for that part of the vector.
The missing piece is still how the TER handles/sanitizes uploaded data. -
Oliver Hader changed priority
Should haveMust have 07/25/22, 11:12 -
Oliver Hader changed target version 07/25/22, 11:13
-
Oliver Hader commented 09/05/22, 17:30
Did not manage to exploit this via upload:
<version version="9.9.0"> <title>The Official TYPO3 Cross-Site Scripting Package</title> <description>This package provides XSS by using scriptalert(12345)/script</description> <state>stable</state> <reviewstate>0</reviewstate> <category>distribution</category> ... <version version="9.9.1"> <title>The Official TYPO3 Cross-Site Scripting Package</title> <description>&lt;script&gt;alert(2)&lt;/script&gt; ![CDATA[scriptalert(12345)/script &lt;script&gt;alert(3)&lt;/script&gt;]]</description> <state>stable</state> <reviewstate>0</reviewstate> <category>distribution</category>ext_emconf.phphas not been sanitized/modied- but the creation of
extensions.xmlused a corresponding sanitization,
at least since January 2017 (I did not track earlier changes in other locations), see https://git.typo3.org/services/t3o-sites/extensions.typo3.org/ter/-/blame/c755d1df7b9e7cd41d969e14bc8e66077f7c753a/html/typo3conf/ext/ter/class.tx_ter_helper.php?page=1#L527-533
-
Oliver Hader commented and changed status
AcceptedNeeds Feedback priorityMust haveShould have 09/05/22, 17:33After analyzing the behavior of the actual TER, I don’t see a real attack vector anymore. I’d opt for fixing this in public, what do you think?
-
Frank Nägler commented 09/05/22, 17:37
I am OK with fixing it in public.
The sanitizer looks a bit weird, I think there are better ways to handle XML or data in XML, but your test proves that no vector exists, so let’s fix it public.
-
Torben Hansen commented 09/06/22, 05:34
Since the issue can not be exploited using the TER extension upload, a fix in public is also OK for me.
-
Oliver Hader changed target version 09/06/22, 06:21
-
Oliver Hader commented and changed project id subject
XSS in distribution overviewHarden distribution overview in extension manager category target version Field 12Frank NäglerField 179.0, 10, 1109/14/22, 06:19→ moved from security tracker to public core tracker
-
Gerrit Code Review pushed patch set 1 for main to change 85260 status
Needs FeedbackUnder Review 07/15/24, 13:32 -
Gerrit Code Review pushed patch set 1 for 12.4 to change 85203 07/16/24, 11:25
-
Georg Ringer commented and changed status
Under ReviewResolved done0 %100 % 07/16/24, 11:30Applied in changeset commit:b639beaea72e28ae30f0133ba035077e4dbbdbd0.
-
Gerrit Code Review pushed patch set 2 for 12.4 to change 85203 status
ResolvedUnder Review 07/19/24, 06:19 -
Georg Ringer commented and changed status
Under ReviewResolved 07/19/24, 06:35Applied in changeset commit:d325006b19c1c3b16768180b7289f50ea4643567.
-
Benni Mack changed status
ResolvedClosed 10/15/24, 09:30


Did not manage yet to test it with extensions.typo3.dev (it does not accept files).
In case
descriptionand other meta-data is passed as is via TER upload → extensions.xml → local XML import, this is a severe XSS vulnerability effecting all TYPO3 sites.https://nvd.nist.gov/vuln-metrics/cvss/v3-calculator?vector=AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:H/A:N/E:H/RL:O/RC:C&version=3.1 (7.8, high)