#102690Script generated with "removeDefaultJS = external" has no nonce attribute
Simon Würstle 12/18/23, 12:11 updated 11/10/26, 12:27

Description
If you enable [SYS][features][security.frontend.enforceContentSecurityPolicy] and set “config.removeDefaultJS” to “external” (= default), the script tag has no “nonce” attribute and thus the script is blocked by the browser.
Reviews 2


Files 2

History 410
-
Gerrit Code Review pushed patch set 1 for main to change 82204 status
NewUnder Review <span data-processor="relativetime" data-value="2023-12-18T15:32:28+00:00" > 12/18/23, 15:32 </span> -
Gerrit Code Review pushed patch set 2 for main to change 82204 <span data-processor="relativetime" data-value="2023-12-19T05:08:19+00:00" > 12/19/23, 05:08 </span>
-
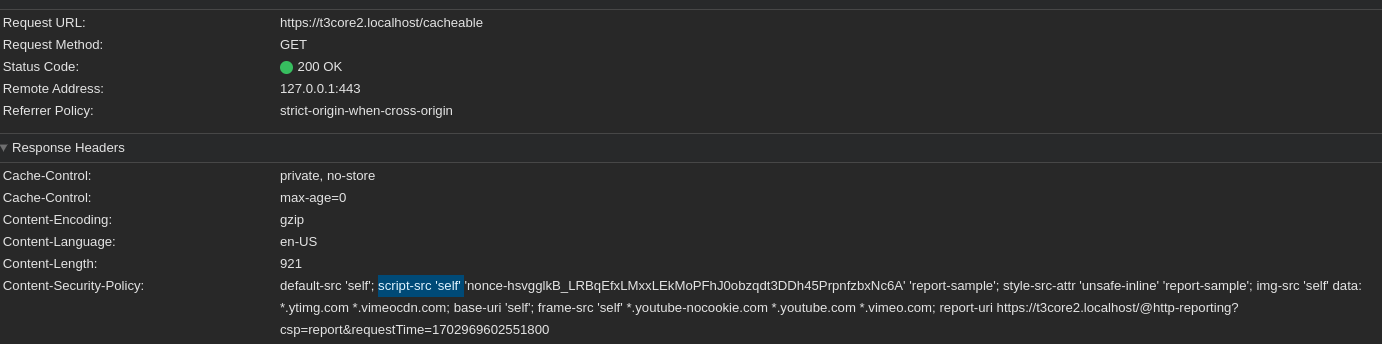
Benjamin Franzke commented and changed attached csp-script-example.png status
Under ReviewNeeds Feedback <span data-processor="relativetime" data-value="2023-12-19T07:14:09+00:00" > 12/19/23, 07:14 </span> -
Simon Würstle commented and changed attached Screenshot 2023-12-19 104916.png <span data-processor="relativetime" data-value="2023-12-19T09:49:55+00:00" > 12/19/23, 09:49 </span>
Of course, this is my csp.yaml:
inheritDefault: true
mutations:
  - mode: extend
    directive: 'script-src'
    sources:
      - "'strict-dynamic'"
The error is:
Answers to your questions:
“Refused to load the script ‘https://foobar.ddev.site/typo3temp/assets/js/ba19e614c16923a947df5b199324c770.js?1694955793’ because it violates the following Content Security Policy directive: “script-src ‘self’ ‘nonce-e0E_2ThWz9pRG8NgCXsiWt59tHyzQ1pHKmPRbF9zEUtMVqV-O9uOyg’ ‘strict-dynamic’ ‘report-sample’”. Note that ‘strict-dynamic’ is present, so host-based allowlisting is disabled. Note that ‘script-src-elem’ was not explicitly set, so ‘script-src’ is used as a fallback.”- it is the script you mentioned (EXT:frontend/Resources/Public/JavaScript/default_frontend.js)
- see attached screenshot
- no CDN
-
Benjamin Franzke commented and changed status
Needs FeedbackAccepted <span data-processor="relativetime" data-value="2023-12-19T11:01:49+00:00" > 12/19/23, 11:01 </span>understood, thanks!
So
strict-dynamicagain – we already have some implications forstrict-dynamicin place, but obviously not enough:
https://github.com/TYPO3/typo3/blob/main/typo3/sysext/core/Classes/Security/ContentSecurityPolicy/SourceKeyword.php#L60-L66Ideally would could apply the
strict-dynamicimplications also during rendering – like `@useNonceIfStrictDynamic@`
CC @ohader -
Garvin Hicking commented and changed category assigned to Oliver Hader <span data-processor="relativetime" data-value="2024-07-31T10:05:35+00:00" > 07/31/24, 10:05 </span>
(Set a category and moved the assignee to Oliver Hader, I hope that’s ok – please drop and let me know if I overstepped :) )
-
Gerrit Code Review pushed patch set 3 for main to change 82204 status
AcceptedUnder Review <span data-processor="relativetime" data-value="2024-10-18T14:07:43+00:00" > 10/18/24, 14:07 </span> -
Gerrit Code Review pushed patch set 4 for main to change 82204 <span data-processor="relativetime" data-value="2025-01-15T11:44:19+00:00" > 01/15/25, 11:44 </span>
-
Gerrit Code Review pushed patch set 5 for main to change 82204 <span data-processor="relativetime" data-value="2026-03-17T11:00:05+00:00" > 03/17/26, 11:00 </span>
-
Gerrit Code Review pushed patch set 5 for main to change 96337 <span data-processor="relativetime" data-value="2026-11-10T12:27:14+00:00" > 11/10/26, 12:27 </span>


Can you share your CSP Policy and the exact CSP error you get?
Questions:
EXT:frontend/Resources/Public/JavaScript/default_frontend.jswhich is used for email links or another one? (I’m asking because the proposed fix accounts for the mentioned case)csp-script-example.png